
DAILY BRIEFING
BeyondTrust Zero-Day Exploited by Armory Castle; AI Decision Models Enter SOC Platforms
Today's briefing covers an exploited BeyondTrust zero-day vulnerability and the rapid adoption of AI decision models across security operations platforms.
5 stories2 min read
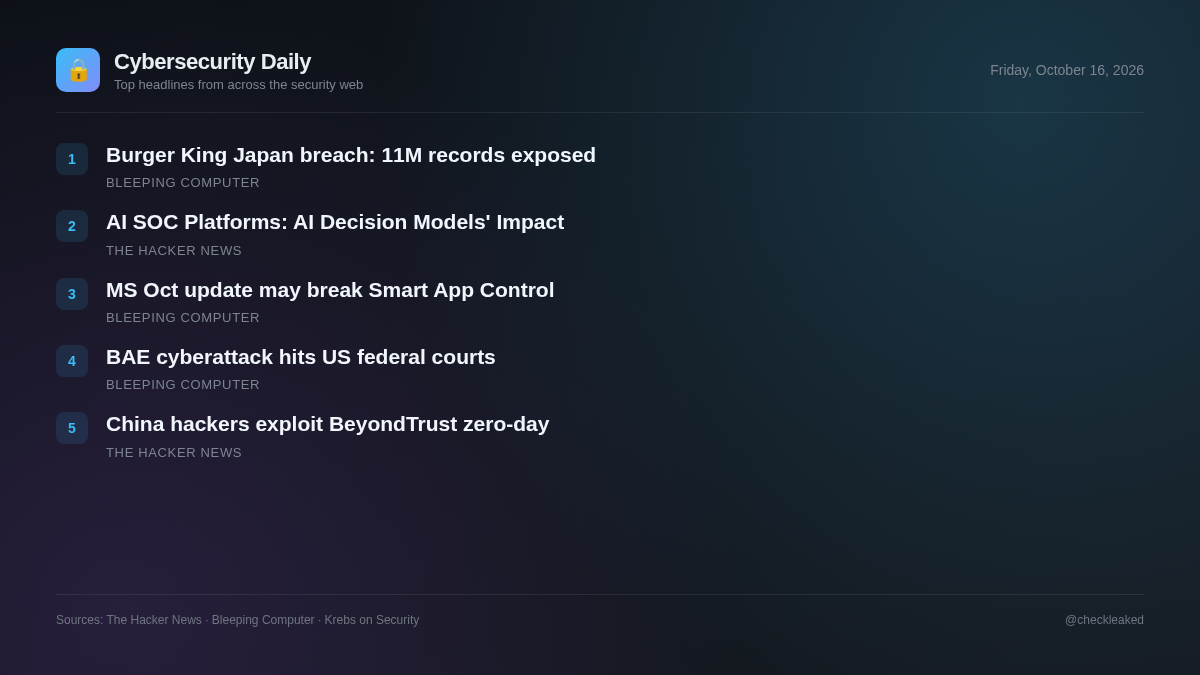
Threat actors associated with China-linked espionage group Armory Castle actively exploited a zero-day vulnerability in BeyondTrust Remote Support appliances prior to patch availability. The flaw allowed unauthorized remote file operations on vulnerable appliances.
At the same time, security operations teams are evaluating non-text AI decision models from providers including TypeSafe AI, OpenAI, and Cribl designed to accelerate fast decision-making in SOC environments.
China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers
China-linked group Armory Castle exploited zero-day flaw CVE-2026-102764 (CVSS 9.3) in BeyondTrust Remote Support to perform unauthorized remote file operations.
- What to do
- Apply the BT26-05-RS patch or upgrade older BeyondTrust Remote Support instances.
Burger King Japan data breach exposes 11 million customer records
Burger King Japan, the Japanese subsidiary of global fast-food giant Burger King, disclosed a major data breach after attackers accessed a server containing 11.18 million customer records.
Microsoft: October Windows update may break Smart App Control
Microsoft says some users may have trouble turning on Smart App Control after installing this month's KB5127648 Windows 11 security update.
BAE Systems cyberattack disrupts US federal court operations
A cyberattack targeting BAE Systems reportedly impacted US federal court operations, though the provided context only returns a Cloudflare verification page.
AI Decision Models and Their Impact on AI SOC Platforms
AI decision models, including TypeSafe AI Jev, OpenAI Decisions API, and Cribl cribl-decision, pass state and typed questions directly to generate scores or choices without text generation.
- Why it matters
- Security operations platforms can leverage non-text AI decision models to directly process system state and automate operational triage.
Key takeaways
- Armory Castle exploited zero-day vulnerability CVE-2026-102764 in BeyondTrust Remote Support before patches were released.
- Self-hosted BeyondTrust Remote Support versions 24.3.1 to 26.2.3 require the BT26-05-RS patch to prevent unauthorized file operations.
- BeyondTrust SaaS instances received automatic updates for CVE-2026-102764 as of October 9, 2026.
- SOC platforms are adopting non-text AI decision models like TypeSafe AI Jev, OpenAI Decisions API, and cribl-decision.