
DAILY BRIEFING
Danfoss Controller Attacks Heat Supermarket Fridges as LG TVs Face Root Flaw
Today's briefing covers attacks targeting Danfoss refrigeration controllers in France, pre-auth root exploits on LG smart TVs, and SAP security warnings.
5 stories2 min read
At the same time, security researchers disclosed three webOS vulnerabilities allowing unauthenticated root access on LG smart TVs via local networks. System administrators and network security teams must prioritize isolating exposed industrial control interfaces and updating vulnerable connected endpoints.
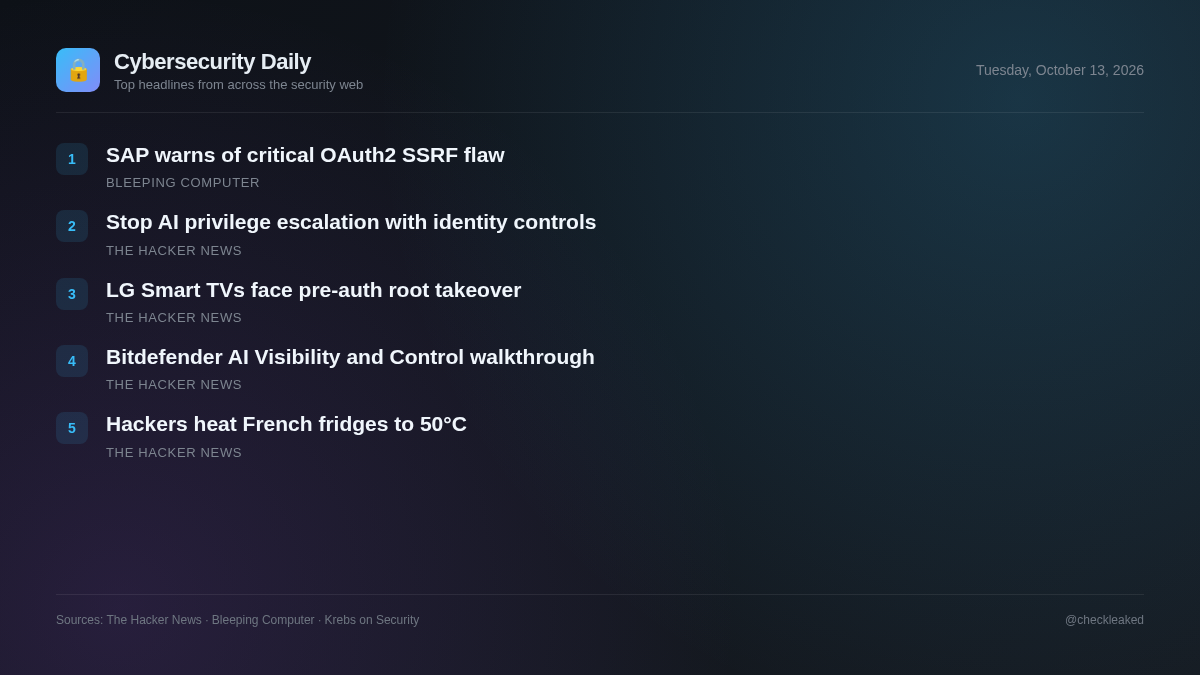
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers
Attackers remotely hijacked Danfoss AK-SM and AK-SC refrigeration controllers across French supermarkets, putting units into defrost modes reaching 50°C and destroying food inventory.
- Why it matters
- Internet-exposed industrial control devices managing physical infrastructure can be manipulated remotely, causing severe financial and operational damage.
- What to do
- Disconnect Danfoss AK-SM and AK-SC controllers from the public internet or strictly filter network access.
SAP warns of maximum severity OAuth2 SSRF security flaw
SAP has addressed 20 security flaws across multiple products in its October 2026 security updates, including a maximum-severity vulnerability in the Cloud SDK for Python.
LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
Three vulnerabilities in LG webOS 7.5.7-25 on firmware 04.54.40 can be chained over local network port 3001 to gain root access on smart TVs without owner interaction or PIN authentication.
- Why it matters
- Local attackers can bypass PIN prompts using trusted test certificates in the sync-demo app to acquire privileged keys and hijack TV operations.
- What to do
- Update affected LG smart TV firmware to the latest patched release immediately.
[Webinar] How to Stop AI-Driven Privilege Escalation With Runtime Identity Controls
Traditional identity controls focused solely on authentication and static access permissions are falling behind as AI accelerates attacker reconnaissance and privilege escalation speed.
- What to do
- Evaluate runtime identity controls to continuously monitor and restrict post-authentication activity.
Product Walkthrough: Bitdefender AI Visibility and Control
Bitdefender introduced GravityZone AI Visibility and Control to track unauthorized AI software, browser-pasted data, editor extensions, and local model runtimes operating on Windows endpoints.
Key takeaways
- Disconnect or strictly filter remote network access to Danfoss AK-SM and AK-SC refrigeration controllers following attacks in France.
- Update LG smart TVs running webOS to patch three chained local network vulnerabilities that permit pre-authentication root access.