
DAILY BRIEFING
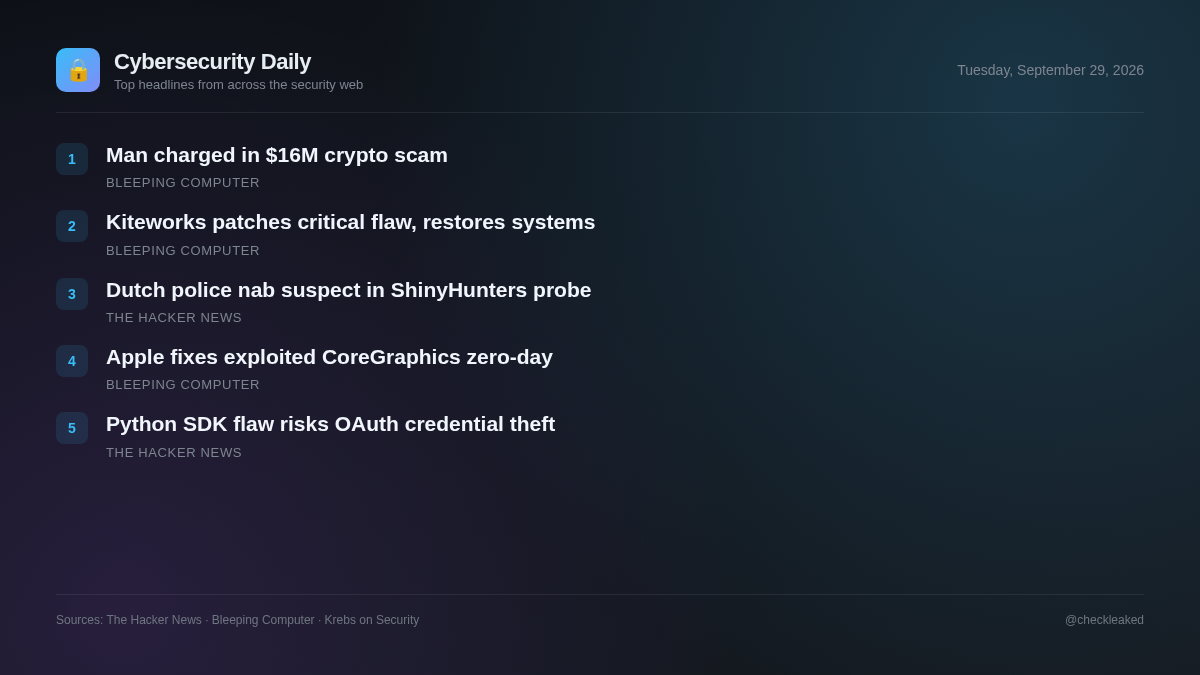
Vietnamese man charged in $16 million 'pig butchering' crypto scam
Dutch police arrest a suspected ShinyHunters member as developers face an OAuth credential leak flaw in the MCP Python SDK.
5 stories2 min read
Dutch law enforcement has taken a suspected ShinyHunters affiliate into custody, marking a major update in long-running investigations into high-profile data theft and extortion operations.
At the same time, developers using the official MCP Python SDK face a high-severity security flaw that could allow untrusted servers to harvest OAuth credentials and compromise linked user accounts. Security teams building or managing integrations around this protocol must review their deployments immediately to secure authorization workflows.
Kiteworks patches critical flaw, brings customer systems online
American tech company Kiteworks has lifted a precautionary advisory asking customers to shut down systems after patching a critical vulnerability.
- Why it matters
- Critical vulnerabilities in enterprise managed file transfer solutions risk server compromise and unauthorized data access.
Apple patches CoreGraphics zero-day flaw exploited in attacks
Apple released security updates to fix a zero-day vulnerability exploited in "extremely sophisticated" targeted attacks on iOS devices.
- Why it matters
- Zero-day vulnerabilities exploited in the wild pose immediate security risks to unpatched devices running affected operating systems.
Official MCP Python SDK Flaw Can Let Malicious Servers Steal OAuth Credentials
A high-severity vulnerability in the official MCP Python SDK allows a malicious server to extract OAuth client secrets, authorization codes, and PKCE proof keys. Attackers can use the stolen credentials to obtain access tokens with the app's full permissions. The issue is fixed in versions 1.30.0 and 2.2.0.
- Why it matters
- AI applications integrated with malicious or compromised MCP servers can lose long-lived OAuth credentials, leading to account takeovers.
Dutch Police Arrest 24-Year-Old Amsterdam Man in ShinyHunters Investigation
Dutch police arrested 24-year-old Pepijn van der Stap in Amsterdam in connection with the ShinyHunters cybercrime group. Van der Stap, previously apprehended in 2023 for data theft and extortion, is scheduled to appear in court in Rotterdam.
- Why it matters
- Law enforcement actions target key figures linked to prominent cybercrime and data extortion groups.
- What to do
- Review external attack surfaces and strengthen data breach monitoring procedures.
Vietnamese man charged in $16 million 'pig butchering' crypto scam
A Vietnamese national was charged with money laundering for his role in a massive "pig butchering" scam, which defrauded a victim out of $16 million worth of cryptocurrency.
Key takeaways
- Dutch police arrested 24-year-old Pepijn van der Stap in Amsterdam in connection with the ShinyHunters group.
- The suspect is scheduled to appear before the Rotterdam District Court on September 29, 2026.
- Maintainers fixed the MCP Python SDK OAuth exposure in versions 1.30.0 and 2.2.0.