
DAILY BRIEFING
Windows 11 24H2 Home and Pro reach end of support in October
Today's briefing covers critical vulnerabilities in DNS resolvers, OS end-of-support timelines, and modern exposure management methodologies.
5 stories2 min read
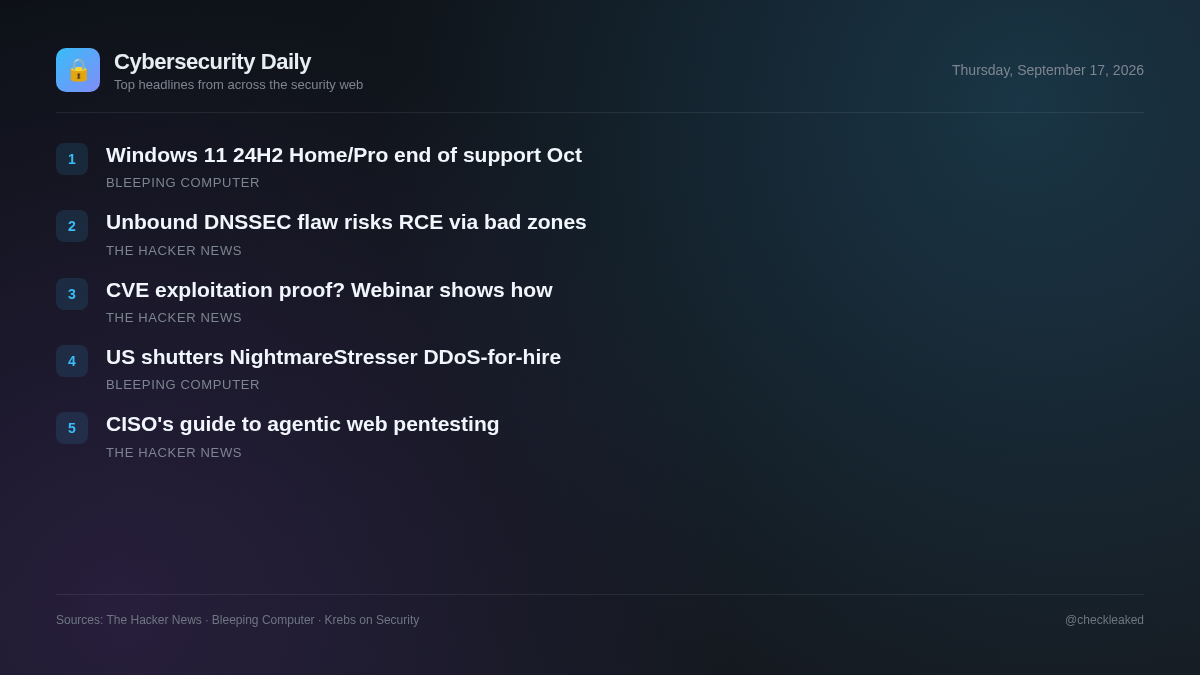
Critical infrastructure software continues to face remote code execution risks, highlighted today by severe heap overflow vulnerabilities discovered in Unbound DNS resolvers. Systems administrators running affected installations need to prioritize immediate software updates to prevent potential exploit chains via malicious DNS responses.
At the same time, security teams face growing operational pressure due to the compression of time between public vulnerability disclosure and real-world exploit development. Organizations are re-evaluating traditional periodic assessments in favor of continuous risk validation and AI-driven security testing frameworks.
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone
NLnet Labs released Unbound 1.26.1 to address a critical heap overflow in its DNSSEC validator (CVE-2026-81642) allowing remote code execution via malicious DNS zones. The release also fixes CVE-2026-82717, a heap corruption flaw in CNAME synthesis that can lead to RCE under specific conditions.
- Why it matters
- Unbound resolvers prior to version 1.26.1 are vulnerable to remote code execution triggered by queries to attacker-controlled DNS zones without requiring privileges or user interaction.
CISO's Expert Guide to Agentic Pentesting for Websites
Reflectiz released a guide discussing the rise of agentic pentesting, highlighting how autonomous AI systems and continuous programmatic testing assist security teams in finding and remediating web vulnerabilities faster than periodic manual engagements.
- Why it matters
- With attackers weaponizing vulnerabilities rapidly, periodic testing leaves large portions of web assets unexamined, whereas autonomous AI testing requires strong guardrails, coverage, and audit trails.
- What to do
- Review web application testing strategies to assess continuous testing requirements and guardrails.
Windows 11 24H2 Home and Pro reach end of support in October
Microsoft reminded customers this week that devices running Windows 11 24H2 Home and Pro editions will stop receiving updates next month.
Can You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This Webinar
A new CVE drops.
US takes down NightmareStresser DDoS-for-hire platform
The U.S.
Key takeaways
- Validate vulnerability exploitability within local environments rather than prioritizing remediation based on CVSS severity scores alone.