
DAILY BRIEFING
Critical Flaws Disclosed in Xen Hypervisor and Ruby on Rails Active Storage
Today's briefing covers critical vulnerabilities in the Xen Hypervisor and Ruby on Rails, alongside operational challenges in securing AI agent runtimes.
5 stories2 min read
Infrastructure security teams must prioritize urgent patching today as critical vulnerabilities affect core components across cloud virtualization and web application frameworks.
Organizations should focus immediate remediation efforts on applying available security patches to hypervisor nodes and web application dependencies, while evaluating runtime visibility over automated AI workflows.
Critical Rails Flaw Lets Attackers Write Server Files via Crafted ImageMagick Uploads
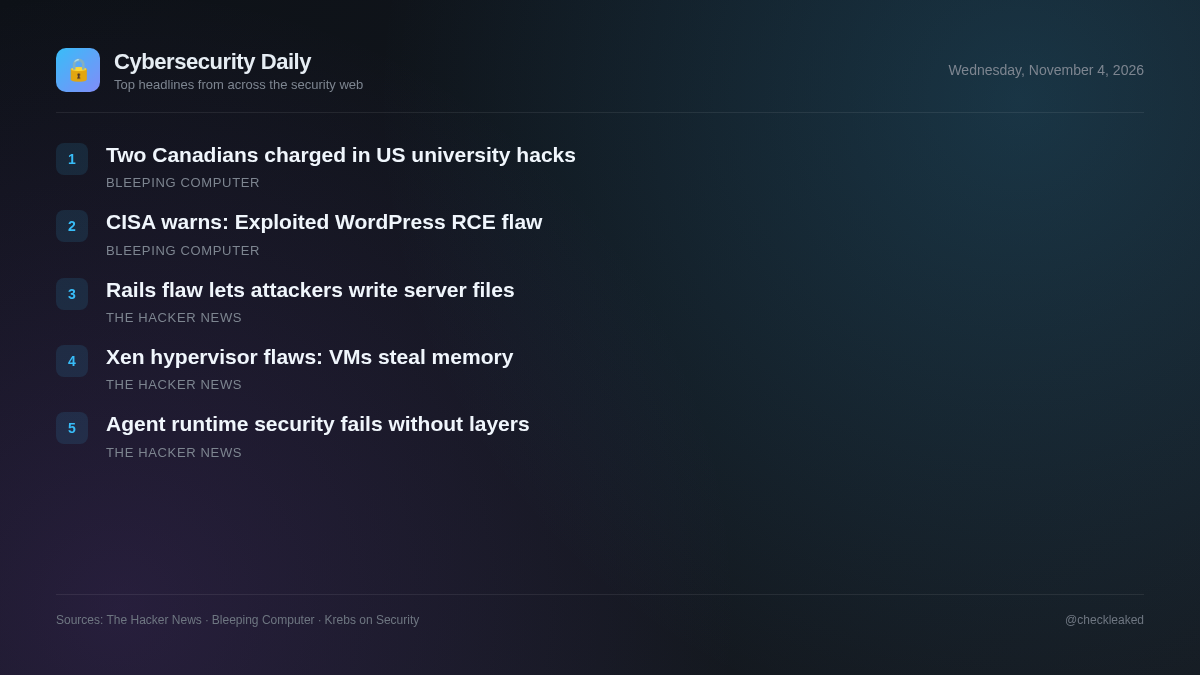
A critical 9.8 CVSS vulnerability in Ruby on Rails Active Storage allows unauthenticated attackers to write or read arbitrary server files via crafted ImageMagick uploads. Fixed in Rails versions 8.1.4.1 and 8.0.5.2.
- Why it matters
- Attackers can read app credentials and secret_key_base files from disk service storage, potentially leading to full remote code execution and lateral movement.
Xen Hypervisor Flaws Let One Malicious VM Read and Write Any Other VM's Memory
Two flaws tracked under CVE-2026-102703 and CVE-2026-102704 (XSA-523) in Xen Hypervisor grant copy operations allow a malicious guest VM to read and write memory across other VMs, including dom0. Versions 4.6 and onward are affected.
- Why it matters
- Hypervisor guest escape risks complete compromise of host memory and cross-tenant data confidentiality in multi-tenant or cloud environments.
CISA flags WordPress RCE flaw as actively exploited in attacks
The US Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies that attackers have started exploiting a recently patched high-severity WordPress vulnerability in the wild.
Radio With No Radar: Why Agent Runtime Security Fails Without the Layers Beneath It
Enterprise AI agents operating outside central security gateways can route actions through unmonitored shadow channels, exposing organizations to policy bypass and data leakage without traditional prompt injections or jailbreaks.
- Why it matters
- Without explicit visibility and runtime guardrails on integrated tools, AI assistants may execute unapproved workflows using personal or non-sanctioned accounts.
US charges two Canadians accused of hacking US universities
A federal grand jury indicted two Canadians suspected of hacking multiple US universities and using the compromised systems to mine for cryptocurrency.
Key takeaways
- Patch Xen hypervisors (versions 4.6 and newer) against CVE-2026-102703 and CVE-2026-102704 to prevent VM memory isolation breaches.
- Update Ruby on Rails to versions 8.1.4.1 or 8.0.5.2 to fix Active Storage ImageMagick arbitrary file write flaw GHSA-f3w6-w445-fwh9.