
DAILY BRIEFING
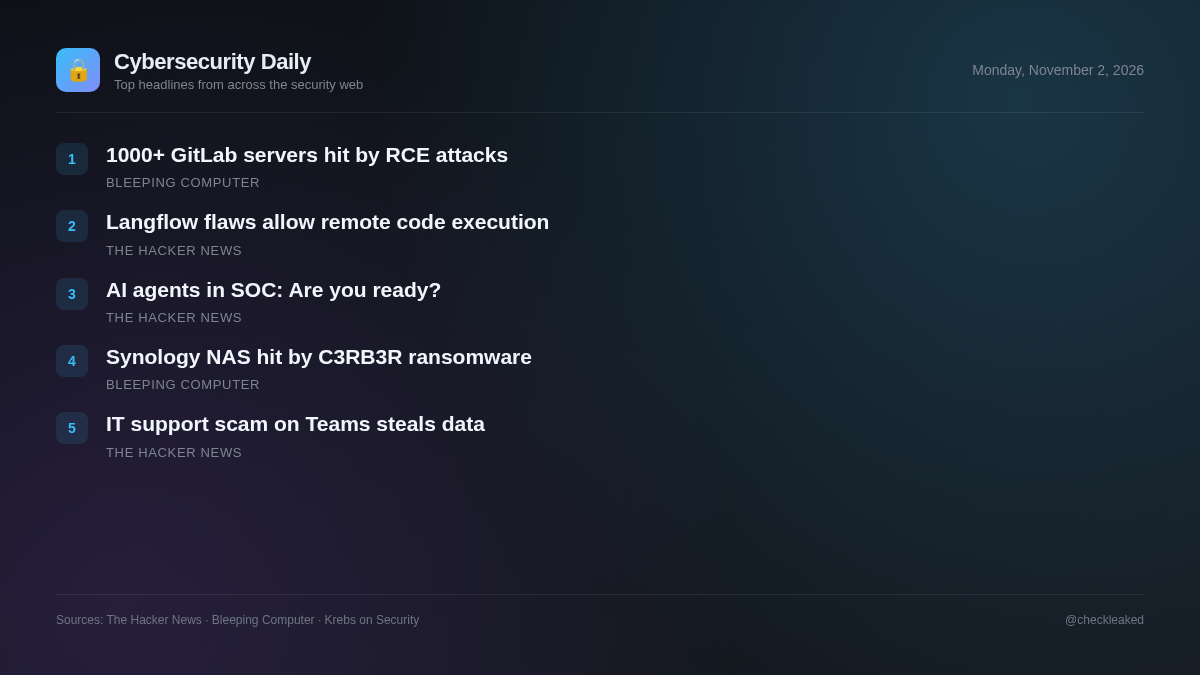
Over 1,000 GitLab servers vulnerable to ongoing RCE attacks
Today's briefing highlights critical unauthenticated RCE flaws in Langflow, social engineering attacks via Microsoft Teams abusing AD CS, and AI agent maturity considerations for SOCs.
5 stories2 min read
Today's vulnerability and threat intelligence reports underscore the twin risks of unauthenticated infrastructure flaws and targeted social engineering. Organizations maintaining AI application workflows must address severe unauthenticated remote code execution vulnerabilities recently disclosed in Langflow, which impact all releases prior to version 1.13.0.
Security teams must prioritize patching AI framework tools and hardening Active Directory Certificate Services configurations while re-evaluating employee helpdesk verification workflows.
Critical Langflow Flaws Could Let Unauthenticated Attackers Run Code on Servers
Two critical flaws in Langflow could let a remote attacker with no account bypass authentication or run arbitrary code, IBM said last week.
- Why it matters
- Unauthenticated remote attackers can bypass security controls or execute arbitrary code on servers hosting Langflow AI agent workflows.
Attackers Pose as IT Support on Microsoft Teams, Abuse AD CS to Steal Company Data
Attackers impersonating IT help desk personnel on Microsoft Teams leveraged Quick Assist to gain remote desktop control of employee PCs. They subsequently exploited insecure Active Directory Certificate Services (AD CS) settings (ESC1/ESC8 paths) to obtain privileged login certificates and exfiltrate corporate data.
- Why it matters
- Insecure AD CS configurations allow social engineering intrusions to escalate to full domain controller account compromise and enterprise data exfiltration.
Over 1,000 GitLab servers vulnerable to ongoing RCE attacks
Over 1,000 Internet-exposed GitLab servers are still unpatched against a maximum-severity flaw actively exploited in remote code execution attacks.
Synology warns of C3RB3R ransomware attacks targeting NAS devices
Taiwanese network-attached storage (NAS) appliance maker Synology warned customers to update their devices immediately due to a surge in C3RB3r ransomware attacks.
Is Your SOC Ready for AI Agents? A Maturity Check Before You Deploy
Forty percent of security teams now use AI every day, and another 56% are testing it.
- Why it matters
- Organizations evaluating AI agents in the SOC must establish clear context, access governance, and baseline metrics before delegating alert handling to automated tools.
Key takeaways
- Restrict Quick Assist usage and audit Active Directory Certificate Services (AD CS) templates for insecure certificate request rules.